Take the First Step Toward Cybersecurity Excellence
Why Nexusguard?

Over 15 Years

Trusted by 100+

Protecting 50,000

40+



Learn More About Nexusguard Academy Courses
Understanding DDoS
Understanding Botnets
What is a Botnet?
A botnet is a network of infected devices controlled remotely by an attacker. These devices (computers, servers, IoT cameras, routers) are called "zombies" or "bots."
Device owners often don't know their devices are compromised.
How Botnets Are Built
1. Infection
- Phishing emails with malware
- Exploiting software vulnerabilities
- Brute-forcing weak passwords (especially IoT devices with default credentials)
2. Command & Control (C&C)
- Infected devices connect to attacker's control server
- Attacker issues commands to entire botnet simultaneously
3. Attack Launch
- Thousands or millions of devices attack the target at once
- Appears to come from legitimate sources worldwide
Real-World Example: Bit-and-Piece Attack (Carpet Bombing)
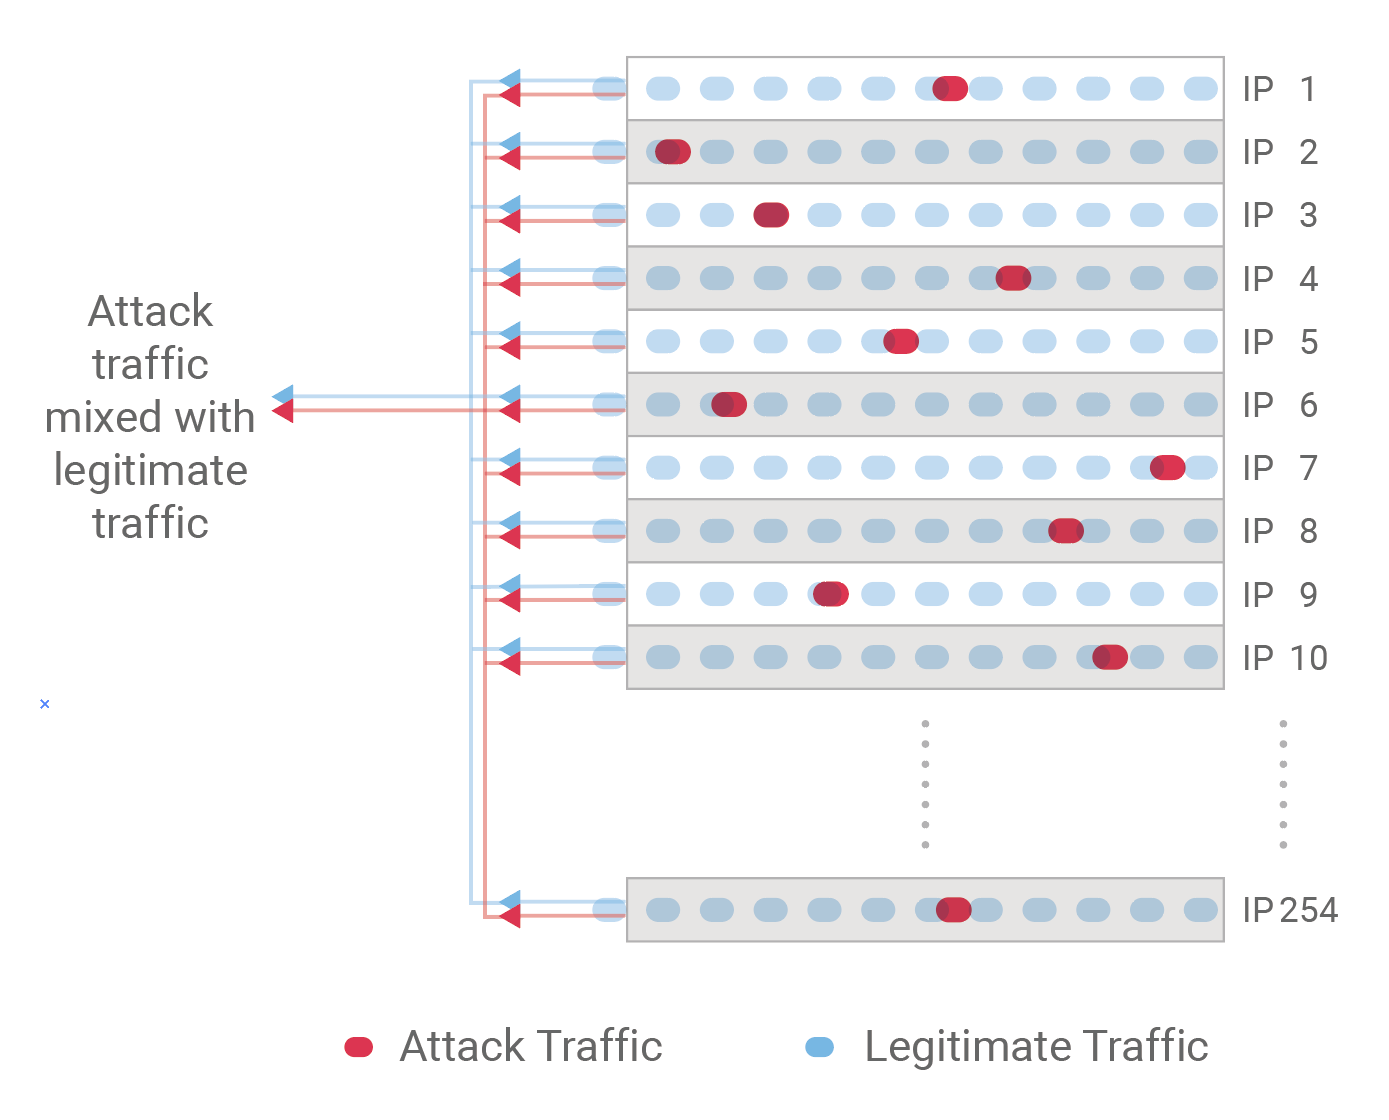
Identified by Nexusguard Research, the bit-and-piece attack (also known as carpet bombing) represents a new breed of stealthy DDoS attacks specifically targeting Communication Service Providers (CSPs) and large networks.
What Makes It Different:
Unlike traditional attacks targeting single IPs, bit-and-piece attacks disperse small pieces of junk traffic across a diverse pool of IP addresses across hundreds of IP prefixes within your network.
How It Works:
- Attack traffic is mixed with legitimate traffic
- Small amounts sent to IP₁, IP₂, IP₃... IP₂₅₄ (hundreds or thousands of IPs)
- Each individual IP receives traffic below detection thresholds
- Traffic converges toward target IP prefix, forming a massive flow
- Easily exceeds capacity limits of generic mitigation devices
Why It's Dangerous:
Detection Challenge:
- Legacy flow-aware devices (firewalls, load balancers, IPS, IDS) often fail to detect these stealthy network layer attacks
- No single IP shows massive traffic spike
- Traffic appears distributed and "normal"
- Detection devices themselves can become bottlenecks
Mitigation Challenge:
- Traditional blackholing (blocking specific IPs) is no longer effective
- Can't block hundreds of destination IPs without blocking legitimate services
- Causes high latency at best, or network deadlock at worst
- Requires advanced network behavior analysis (NBA)
Defense Requirements:
- Traffic anomaly detection across entire IP ranges
- Network behavior analysis (not just per-IP monitoring)
- Cloud-based scrubbing with massive capacity
- Real-time traffic visibility and attack analytics
(Source: Nexusguard, "How to Detect and Mitigate Bit-and-Piece DDoS Attack")
Why Botnets Are Hard to Stop
- Global Distribution: Bots spread across countries and networks
- Legitimate-Looking Traffic: Each bot sends normal requests
- Massive Scale: Modern botnets control millions of devices
- Constantly Evolving: New botnet malware variants appear regularly
Ready to Safeguard Your Web Assets?